🎯 Objective
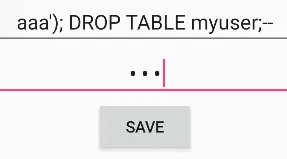
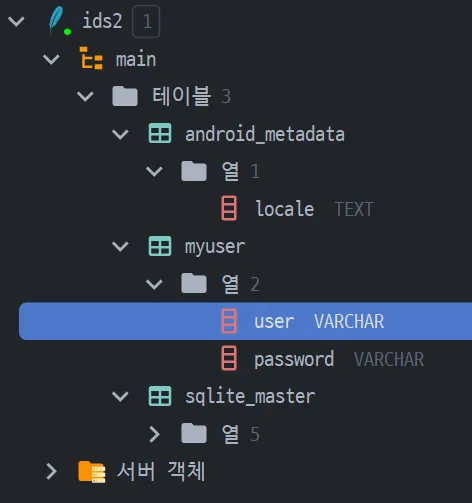
myuser 테이블에 저장된 ID/PW 를 획득하거나, 테이블 구조 자체를 삭제(DROP) 하여 보호장치 없는 DB 저장을 검증하라.
1️⃣ 코드 & 취약점 분석
전체 코드
public class InsecureDataStorage2Activity extends AppCompatActivity {
    private SQLiteDatabase mDB;

    @Override // android.support.v7.app.AppCompatActivity, android.support.v4.app.FragmentActivity, android.support.v4.app.BaseFragmentActivityDonut, android.app.Activity
    protected void onCreate(Bundle savedInstanceState) {
        super.onCreate(savedInstanceState);
        try {
            this.mDB = openOrCreateDatabase("ids2", 0, null);
            this.mDB.execSQL("CREATE TABLE IF NOT EXISTS myuser(user VARCHAR, password VARCHAR);");
        } catch (Exception e) {
            Log.d("Diva", "Error occurred while creating database: " + e.getMessage());
        }
        setContentView(R.layout.activity_insecure_data_storage2);
    }

    public void saveCredentials(View view) {
        EditText usr = (EditText) findViewById(R.id.ids2Usr);
        EditText pwd = (EditText) findViewById(R.id.ids2Pwd);
        try {
            this.mDB.execSQL("INSERT INTO myuser VALUES ('" + usr.getText().toString() + "', '" + pwd.getText().toString() + "');");
            this.mDB.close();
        } catch (Exception e) {
            Log.d("Diva", "Error occurred while inserting into database: " + e.getMessage());
        }
        Toast.makeText(this, "3rd party credentials saved successfully!", 0).show();
    }
}
| 취약 요소 | 영향 |
| 직접 문자열 연결 | 사용자가 ',); DROP …-- 등 SQL 문법 삽입 가능 |
| 입력 검증/인코딩 부재 | SQL Injection → 임의 쿼리 실행, 데이터 변조·삭제 |
| 암호화·해시 부재 | 암호, ID 그대로 평문 SQLite DB 내 보관 |